GitHub security advisory permissions reach general availability in custom repository roles
GitHub now lets organisations delegate repository security advisories and private vulnerability reports through custom roles with narrower access.
- GitHub now lets organisations delegate repository security advisory work through custom repository roles.
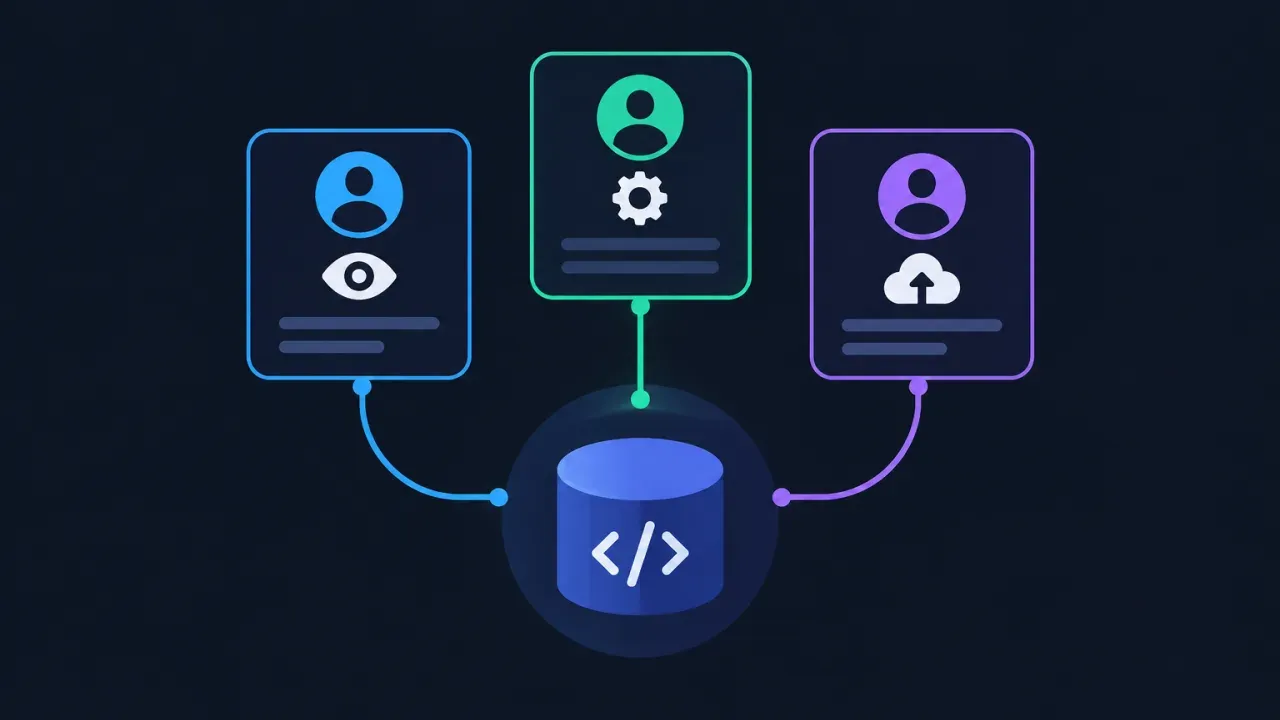
- The new permissions cover viewing, creating, managing, accepting private vulnerability reports, closing or reopening advisories, and publishing advisories or requesting CVEs.
- The permissions apply to repository security advisories and private vulnerability reports, but only on the repositories where access is assigned.
- GitHub says the feature is available on plans that support custom repository roles, including GitHub Enterprise Cloud.
- Some actions still need elevated access: confidential comments require write access as well as Create, Edit, and Manage, and merging from a temporary private fork still needs a repository administrator or security manager.
GitHub has made security advisory permissions generally available for custom repository roles. The change lets organisation owners give people access to repository security advisories and private vulnerability reports without granting repository administrator privileges or the broader organisation-wide security manager role. GitHub announcement
What GitHub is changing
The new permissions sit under Security when you create or edit a custom repository role. GitHub says there are four permission sets: view security advisories; create, edit and manage security advisories; accept private vulnerability reports and close or reopen advisories; and publish security advisories and request CVEs. The company also says these permissions apply to both repository security advisories and private vulnerability reports. GitHub announcement
That makes the feature useful for teams that need to handle advisories inside a specific repository, but do not need access to the rest of an organisation’s security workflow. GitHub says you can assign the role to users and teams only on the repositories where they need it. GitHub announcement
Why it matters
For security and platform teams, the practical win is narrower access. Instead of giving someone broad administrative control just so they can review a private report, edit an advisory or publish a CVE request, org owners can now scope that work to the repositories involved. GitHub explicitly says the permissions can be used so a team can access the repositories they maintain without exposing advisories across the whole organisation. GitHub announcement
That said, this is not full delegation. GitHub keeps some steps gated behind higher privilege. Merging changes from a temporary private fork still requires a repository administrator or security manager. Confidential comments also remain restricted: GitHub says they are only available to people with Create, Edit, and Manage who also have write access to the repository. GitHub announcement; GitHub docs
Who can use it
GitHub says the feature is available to organisations on plans that support custom repository roles, including GitHub Enterprise Cloud. Its documentation states that only organisations on GitHub Enterprise Cloud can create custom repository roles. GitHub announcement; GitHub docs
Permission summary
| Permission set | What it allows | Notable limit |
|---|---|---|
| View security advisories | View draft advisories, status and comments | Cannot create or publish advisories on its own GitHub announcement |
| Create, Edit, and Manage security advisories | Create and edit advisories, comment, manage collaborators, create a temporary private fork | Cannot delete a temporary private fork; confidential comments still need repository write access GitHub announcement |
| Accept private vulnerability reports and close or reopen security advisories | Handle the report workflow and state changes | Requires View or Create, Edit, and Manage permissions GitHub announcement |
| Publish security advisories and request CVEs | Publish advisories and request CVEs | Merging from a temporary private fork still needs repository administrator or security manager access GitHub announcement |
What to watch next
The announcement is about access control, not a redesign of the advisory workflow. The main question for teams is whether their existing role structure can be tightened around advisory handling without blocking the people who actually need to respond. GitHub’s docs point to repository security advisories as the place to start, and the new permissions are designed to keep that work inside the relevant repositories rather than across the whole organisation. GitHub announcement; GitHub docs
For teams already using custom repository roles, the immediate checklist is simple: confirm your organisation plan supports the feature, map which repositories need advisory handling, and decide which of the four permission sets each team actually needs. The point of the change is not more access. It is less of the wrong access.
Before
Teams often needed repository administrator or organisation-wide security manager access to work on repository security advisories and private vulnerability reports.
After
Organisation owners can assign narrower custom repository role permissions for viewing, managing, accepting reports, and publishing advisories on only the repositories that need them.